TACACS+ Provider

Terminal Access Controller Access-Control Systems (TACACS+)

Create TACACS+ Provider

  1. From the left navigation menu, navigate to External Systems > Providers and click Create Provider.
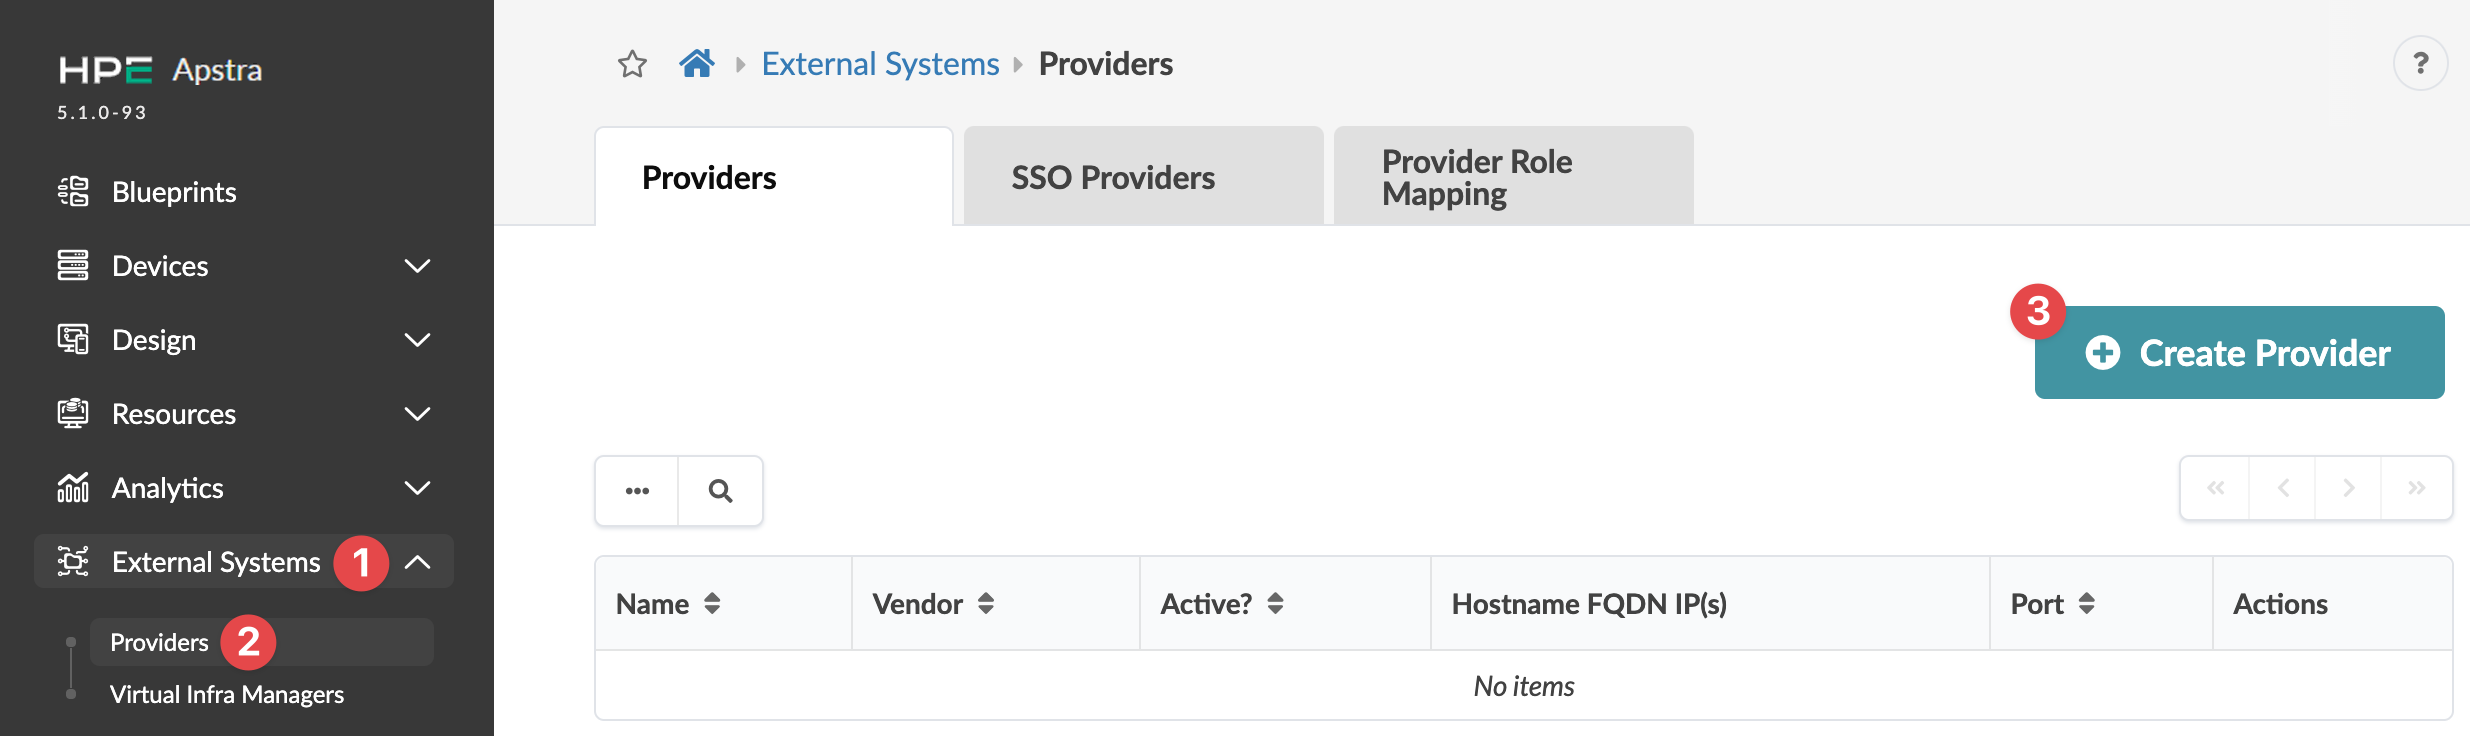
    HPE Apstra 5.1.0-93 interface showing External Systems Providers tab with navigation menu, Create Provider button, and empty table for provider details.
  2. Enter a Name (64 characters or fewer), select TACACS+, and if you want TACACS+ to be the active provider, toggle on Active?.
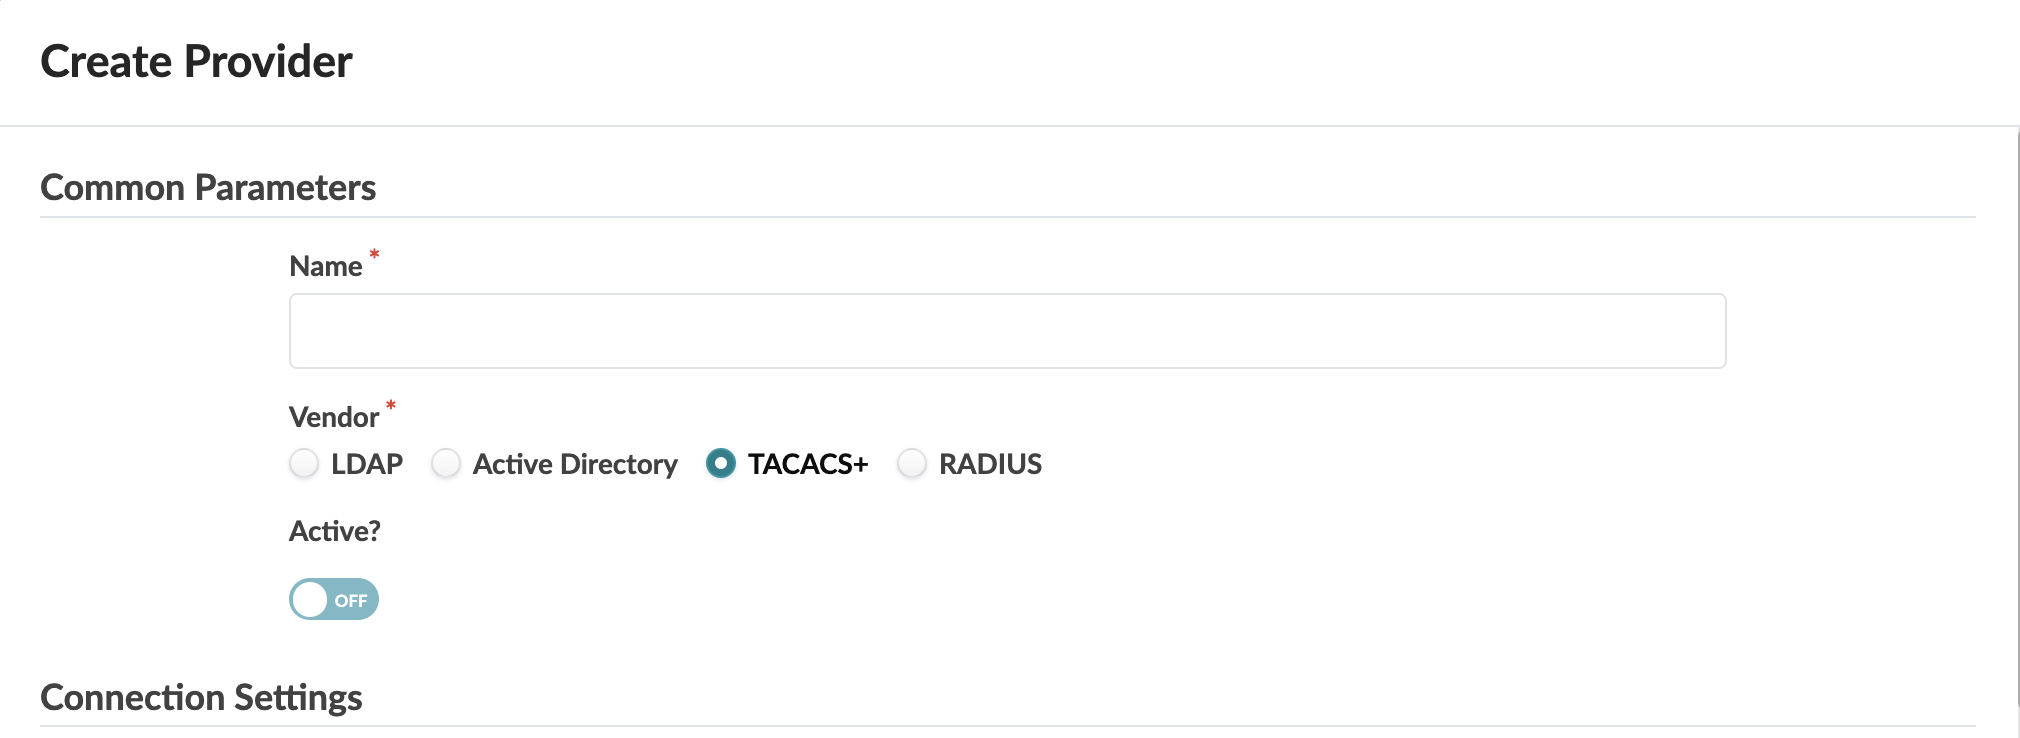
    User interface for creating a provider configuration with fields for Name, Vendor options including TACACS+ selected, and Active toggle set to OFF.
  3. For Connection Settings, enter/select the following:
    • Port - The TCP port used by the server, usually 49
    • Hostname FQDN IP(s) - The fully qualified domain name (FQDN) or IP address of the TACACS+ server. For high availability (HA) environments, specify multiple TACACS+ servers using the same settings. If the first server cannot be reached, connections to succeeding ones are attempted in order.
  4. For Provider-specific Parameters enter/select the following, as appropriate:
    • Shared Key - shared key configured on the server

      Caution

      Shared key is not displayed when editing a configured TACACS+ provider. If you do not change it, the previously configured shared key is retained. If you test the provider and you have not re-entered the shared key, a null shared key is used for the test and may not work.

    • Auth Mode - Authentication mode - ASCII (clear-text), PAP (Password Authentication Protocol), or CHAP (Challenge-Handshake Authentication Protocol)

    • Advanced Configuration

      • Timeout (seconds) - Increasing timeout above the default 30 seconds may impact API responsiveness for all users. If you need a longer timeout for MFA support, you may increase the timeout up to 60 seconds. If you require a timeout above 60 seconds, contact Juniper Technical Support.
  5. You can Check provider parameters and Check login (to verify authentication with the remote user credentials) before creating the provider.
  6. Click Create to create the provider and return to the table view.

Configure TACACS+ Provider

To authorize HPE Networking Apstra Data Center Director users via a TACACS+ provider, the TACACS+ server must be configured to properly return an aos-group attribute. This attribute must be mapped to a defined Apstra DC Director Role. The example configuration below is for the open-source tac_plus TACACS+ server.

The apstra-admins group must be mapped to a defined Apstra Role.

After configuring and activating a provider, you must map that provider to one or more user roles to give access permissions to users with those roles.